Why it matters: CISA says attackers are using the chained Ivanti flaws to run commands remotely without logging in and to steal credentials and data, and it warns that Ivanti's own integrity tool may not detect the intrusions.
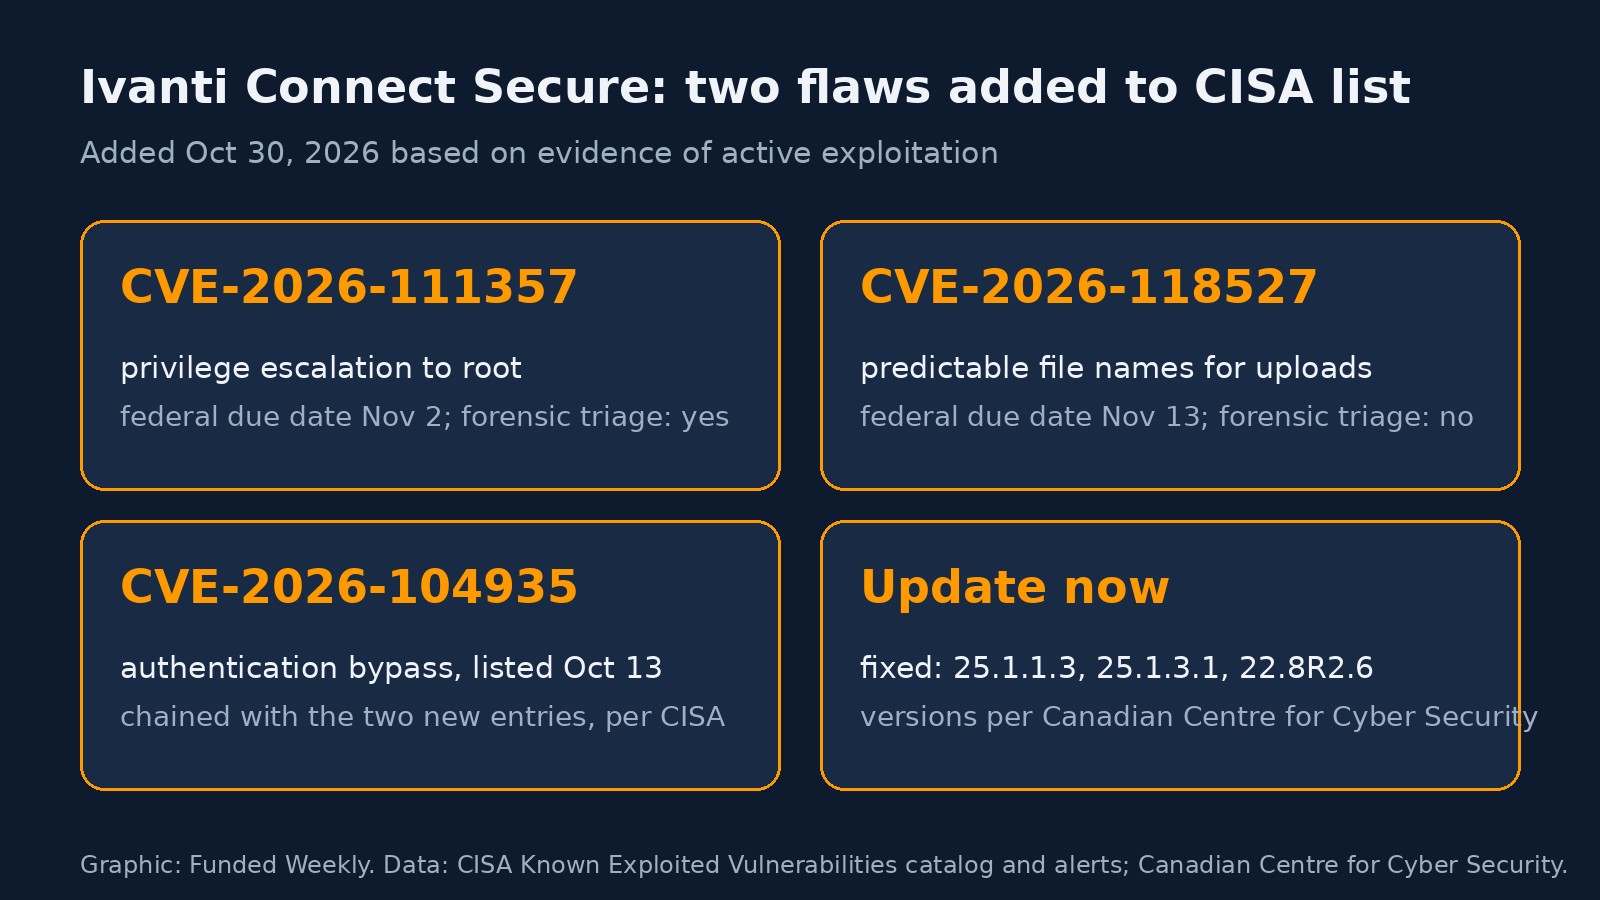
The Cybersecurity and Infrastructure Security Agency added two vulnerabilities in Ivanti Connect Secure to its Known Exploited Vulnerabilities catalog on Oct 30, "based on evidence of active exploitation." Connect Secure is Ivanti's VPN appliance software. CISA's catalog says both can be chained with CVE-2026-104935, an authentication bypass in the same product that it listed on Oct 13.
CVE-2026-111357: CISA describes it as a missing-authentication flaw that could let a local authenticated attacker escalate their privileges. The National Vulnerability Database record says the bug leads to privilege escalation to root and rates it 7.0, High.
- Deadline: CISA gives federal civilian agencies until Nov 2, 2026 to act.
- Forensics: CISA marks this entry as requiring forensic triage, a check under its federal directive for signs that a system was compromised before it was patched.
CVE-2026-118527: CISA says this flaw involves predictable identifiers and allows a remote authenticated attacker to upload files with content the attacker controls to a known location on disk.
- Deadline: The federal due date is Nov 13, 2026, and CISA does not require forensic triage for this entry.
What CISA says is happening: In an updated alert revised Oct 30, CISA says it is aware of threat actors exploiting the three chained flaws, which allow remote, unauthenticated execution of arbitrary commands, to conduct credential theft and data exfiltration. It lists affected versions as 25.1.1.2 and prior, 25.1.2.2 and prior, and 22.8R2.5 and prior and urges organizations to update immediately.
- Fixed versions: The Canadian Centre for Cyber Security lists Connect Secure versions prior to 25.1.1.3, 25.1.3.1 and 22.8R2.6 as affected.
- Detection: CISA warns that Ivanti's Integrity Checker Tool may not detect exploitation of CVE-2026-104935 because the attackers' commands run in memory. CISA says determining whether a system was compromised calls for network and memory forensics.
- If compromised: CISA recommends backing up the configuration, doing a factory reset and upgrade, restoring the configuration, resetting passwords for all accounts and reissuing stored certificates and API keys.
- End of life: CISA notes that Connect Secure version 22.8 reaches end of life on Jan. 31, 2027.
CISA says its directive applies only to federal civilian agencies but encourages all organizations to prioritize fixing vulnerabilities in the catalog.
Sources
- CISA alert: "CISA Adds Two Known Exploited Vulnerabilities to Catalog," Oct 30, 2026
- CISA alert: "CISA Urges Patching Newly Exploited Vulnerabilities in Ivanti Connect Secure," last revised Oct 30, 2026
- CISA Known Exploited Vulnerabilities catalog, entry for CVE-2026-111357 (added Oct 30, 2026)
- CISA Known Exploited Vulnerabilities catalog, entry for CVE-2026-118527 (added Oct 30, 2026)
- National Vulnerability Database: CVE-2026-111357
- Canadian Centre for Cyber Security: Ivanti security advisory (AV26-1035), updated Oct 30, 2026
How we checked this: We read CISA's Oct 30 alert, its updated Ivanti alert (last revised Oct 30), CISA's catalog data file (version 2026.10.30), the National Vulnerability Database record for CVE-2026-111357 and the Canadian Centre for Cyber Security's advisory AV26-1035, in copies saved on Oct 30, 2026 at about 5:07 PM ET, and checked every CVE identifier, version, date and description against them.
See something wrong? Tell us and we'll fix it. Every fix is dated and listed on our Corrections page.