Why it matters: The GitLab flaw lets an unauthenticated user run code on a GitLab server, and CISA requires forensic triage for it, a check for signs that a system was compromised before it was patched.
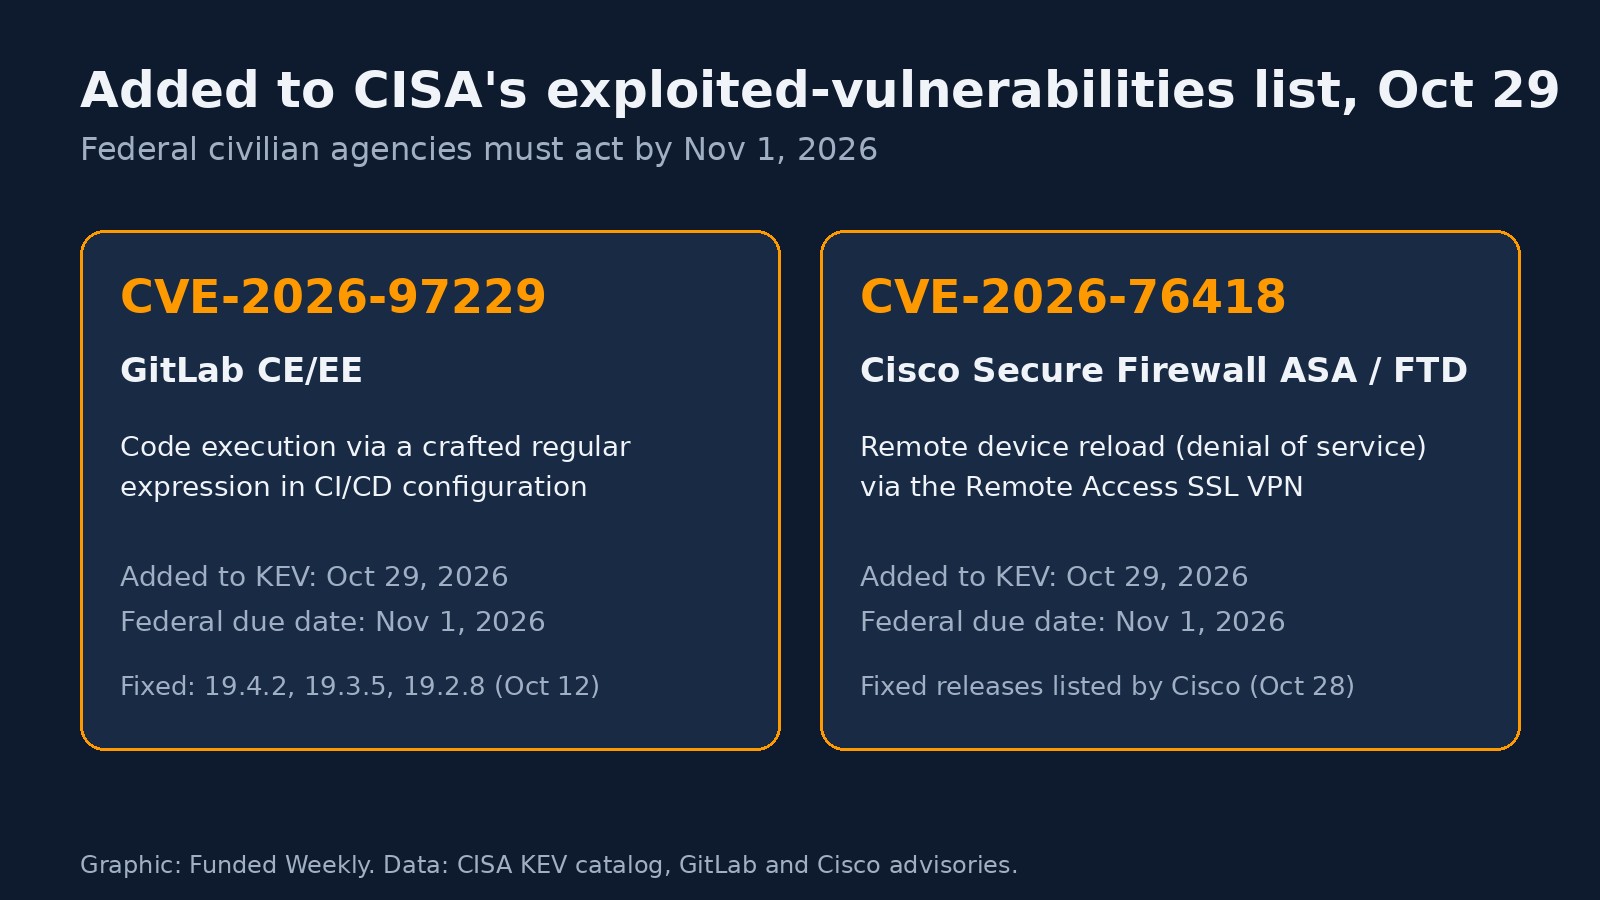
The Cybersecurity and Infrastructure Security Agency added two vulnerabilities to its Known Exploited Vulnerabilities catalog on Oct 29, "based on evidence of active exploitation." One is in GitLab's self-managed software and the other is in Cisco's firewall software. CISA's catalog gives both a federal due date of Nov 1, 2026.
GitLab, CVE-2026-97229: GitLab says the flaw could have allowed an unauthenticated user to execute arbitrary code on the GitLab server through a specially crafted regular expression in a CI/CD configuration. GitLab rated it CVSS 10.0.
- Affected: GitLab Community Edition and Enterprise Edition 19.2 before 19.2.8, 19.3 before 19.3.5 and 19.4 before 19.4.2.
- Fixed: versions 19.4.2, 19.3.5 and 19.2.8, released Oct 12. GitLab says GitLab.com and GitLab Dedicated were already patched, and it has published six threat detections for self-managed customers.
- Ruby: CISA notes that other products can potentially be affected by the same underlying bug in Ruby's regular expression engine. The Ruby project released Ruby 4.0.9, 3.4.12 and 3.3.13 on Oct 23 with the fixes, and says applications are affected only when they compile regular expressions from input an attacker controls.
- CISA's catalog marks the GitLab entry as requiring forensic triage under its directive for federal agencies. CISA's directive sets out when agencies check whether attackers compromised a system before the patch was applied.
Cisco, CVE-2026-76418: Cisco's advisory, first published Oct 28, says a flaw in the remote access VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software could let an unauthenticated, remote attacker make the device reload, causing a denial of service. Cisco rates it High, with a CVSS base score of 8.6.
- Affected: devices running a vulnerable release with the remote access VPN login reachable and secondary authentication configured on a tunnel group.
- Fixed: Cisco lists first fixed releases including ASA 9.20.4.50, 9.22.3.200 and 9.24.1.27, and FTD 7.4.9, 7.6.7 and 10.0.3, among others, in its advisory. It says there are no workarounds, though disabling secondary authentication is a mitigation.
- Cisco says its security team became aware of active exploitation in October 2026. CISA's catalog does not require forensic triage for this entry.
CISA says its directive applies only to federal civilian agencies but encourages all organizations to prioritize fixing vulnerabilities in the catalog.
Sources
- CISA alert: "CISA Adds Two Known Exploited Vulnerabilities to Catalog," Oct 29, 2026
- CISA Known Exploited Vulnerabilities catalog, entry for CVE-2026-97229 (added Oct 29, 2026)
- CISA Known Exploited Vulnerabilities catalog, entry for CVE-2026-76418 (added Oct 29, 2026)
- GitLab: "GitLab Critical Patch Release: 19.4.2, 19.3.5, 19.2.8," Oct 12, 2026
- Cisco security advisory cisco-sa-asaftd-tunnel-dos-s6mgkb75 (CVE-2026-76418), Oct 28, 2026
- Ruby: "Regexp compilation fixes related to GitLab's CVE-2026-89078, CVE-2026-93577, CVE-2026-97229 and CVE-2026-110264," Oct 23, 2026
How we checked this: We read CISA's Oct 29 alert, CISA's catalog data file (version 2026.10.29), GitLab's 19.4.2 patch release notes, Cisco's advisory and Ruby's Oct 23 regexp notice in copies saved on Oct 30, 2026 at about 8:06 AM ET, and checked every CVE identifier, version, date and description against them.
See something wrong? Tell us and we'll fix it. Every fix is dated and listed on our Corrections page.